
Every year, enterprises pour millions of dollars into ERP implementations — and a striking number of them go over budget, miss deadlines, or get abandoned entirely. The Standish Group has tracked this problem for decades, and the pattern is consistent: ERP projects fail not because the software is bad, but because the surrounding decisions are.
Read More
매년 기업들은 ERP 도입에 수십억 원을 쏟아붓습니다. 그리고 놀라울 만큼 많은 프로젝트가 예산을 초과하거나, 일정을 지키지 못하거나, 결국 중단되고 맙니다. 수십 년간 이 문제를 추적해온 Standish Group의 데이터는 일관된 패턴을 보여줍니다. ERP 프로젝트의 실패 원인은 소프트웨어가 나빠서가 아닙니다. 프로젝트를 둘러싼 의사결정이 잘못되었기 때문입니다.
Read More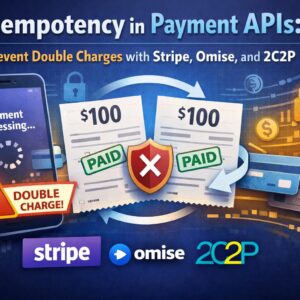
用户点击"立即支付",请求超时,页面没有任何响应——系统接下来会发生什么? 如果Payment API没有实现幂等性,答案可能是:用户被重复扣款。订单被重复创建。Webhook触发后服务器崩溃,库存已经扣减但订单记录从未提交。
Read More
冪等な操作(Idempotent operation)とは、何度実行しても結果が同一となる操作のことである。 Payment APIの文脈では、「課金リクエスト」がタイムアウト・クライアントリトライ・Webhookの重複配信によって何度送信されたとしても、課金は必ず一度だけ、同額で、ユーザーの口座から一回だけ引き落とされることを意味する。
Read More
ลองนึกภาพนี้ — ลูกค้ากดปุ่ม "ชำระเงิน" แล้ว connection หลุดกลางคัน แอปค้าง ไม่มี response กลับมา แล้วระบบของคุณจะทำอะไรต่อ?
Read More
When a customer clicks "Pay Now" and the request times out — what happens next? Without idempotency in your payment API, the answer might be: the customer gets charged twice. Or the order gets created twice. Or the webhook fires, your server crashes mid-process, and now the inventory is decremented but the order row was […]
Read More
あなたのSOCは、アラートの洪水に溺れていないだろうか。 企業のセキュリティオペレーションセンター(SOC)が1日に受信するアラートは平均4,484件、28種類以上のツールから届く。アナリストが1件のアラートを調査するのに平均70分かかり、誰かが最初に確認するまでに56分が経過する。Devo社の「2024 SOC Performance Report」によれば、アラートの53%がfalse positiveであり、約半数は一度も調査されない。
Read More
ทีม SOC ขององค์กรกำลังจมอยู่กับปริมาณ alert ที่ท่วมหัว ศูนย์ปฏิบัติการด้านความปลอดภัย (SOC) ระดับองค์กรโดยเฉลี่ยได้รับ 4,484 alerts ต่อวัน จากเครื่องมือกว่า 28 ระบบ นักวิเคราะห์ใช้เวลาเฉลี่ย 70 นาทีในการตรวจสอบ alert เพียงหนึ่งรายการ และกว่าจะมีคนเปิดดู alert นั้น เวลาก็ผ่านไปแล้ว 56 นาที จากรายงาน Devo SOC Performance Report ปี 2024 พบว่า 53% ของ alerts เหล่านั้นเป็น false positive และเกือบครึ่งหนึ่งไม่เคยถูกตรวจสอบเลย
Read More
Your SOC is getting buried alive. The average enterprise security operations center receives 4,484 alerts per day from 28 or more tools. An analyst spends 70 minutes investigating a single alert — and 56 minutes pass before anyone even looks at it. According to Devo’s 2024 SOC Performance Report, 53% of those alerts are false […]
Read More
历时三周、逐条commit的实录:使用Wazuh 4.x、IRIS-web和自研FastAPI集成器从零搭建生产级安全运营中心——检测规则、告警流水线、IOC情报富化,以及那些永远不会出现在架构图里的基础设施坑点。
Read More